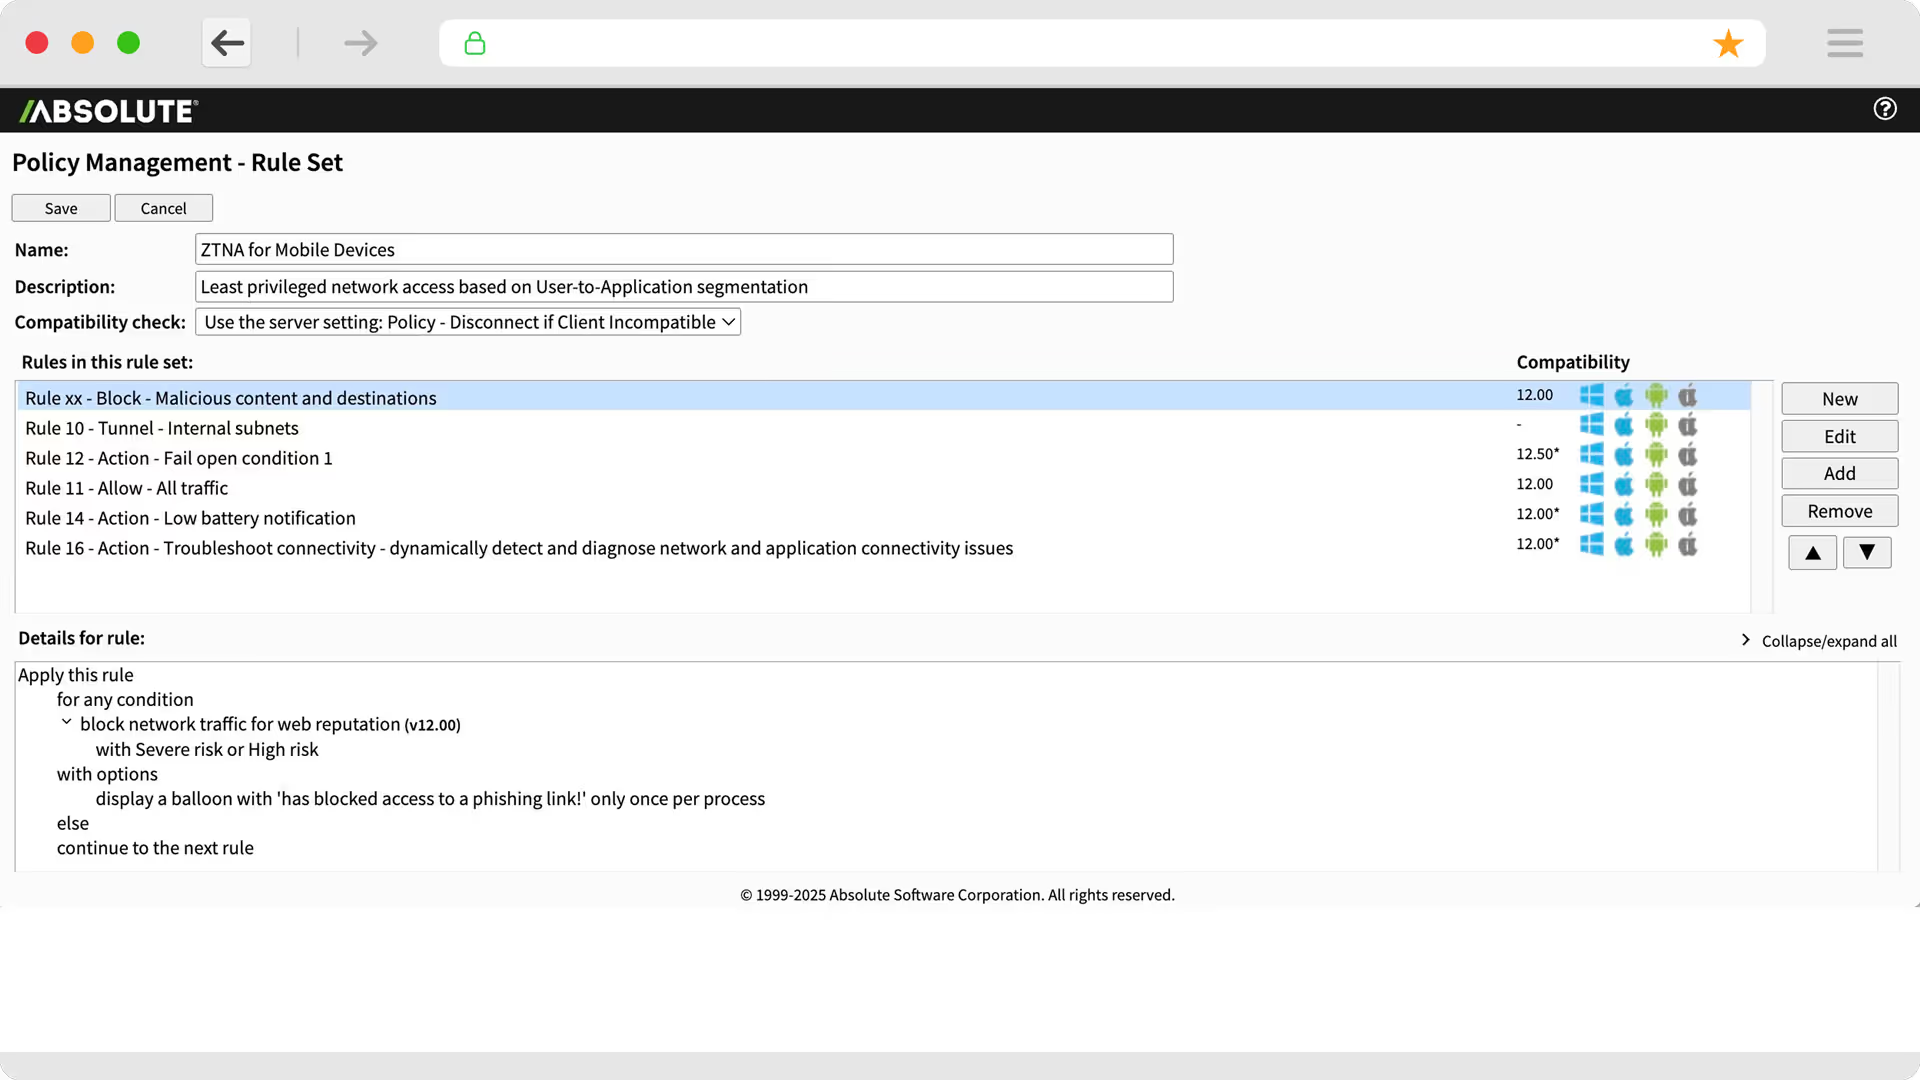
ZTNA solution with optimized tunnel for secure remote access to applications AI-generated from public sourcesThe starting point for every profile: auto-generated by 0-Doubt from public vendor materials, and not yet confirmed by the vendor or an independent analyst. Nothing here is hidden or overstated — it simply has not been reviewed yet.Where every profile starts, before the vendor or an analyst has reviewed it. A higher label means a more independent source — not a better product.How trust works →
Tools & products
Read by an AI model from absolute.com’s own pages. What the vendor says it does, not independently verified.
Integrates with: CrowdStrike ↗, General Dynamics ↗, Informatica ↗, Microsoft ↗, Network Intelligence ↗
Integrated by: Abstract Security, DeviceTotal, Green Hills Software, IONX Solutions, OctoXLabs,
2 of 5 independent trust signals established
Absolute has 2 dimensions with established evidence. The rest have not been confirmed yet.
Not yet established: Independently verified · Disclosure posture · Momentum
Has anyone other than the vendor confirmed this?
1 independent source(s) corroborate this vendor's claims.
Is this a real, durable business?
How long this vendor has been operating, and who stands behind them.
Certifications & compliance claimsWhat the tiers meanVerified in a public registry — we confirmed this against an authoritative public registry (FedRAMP Marketplace, CSA STAR) and re-check it by the registry's own identifier. Stated by the vendor — the vendor says it on a page they control; a sourced claim about themselves, not an independent check. Detected on a page — found during automated enrichment, neither registry-confirmed nor stated on the vendor's own site.
Some certifications have no public registry at all — SOC 2 and HIPAA among them. For those, “not registry-verified” is not a shortfall and means nothing about the vendor.
Detected on a page
Some of these (SOC 2, HIPAA and similar) have no public registry, so no one can independently verify them — that is a fact about the framework, not about this vendor.
Security headers (5/5) — checked 10/18/2026
No outages recorded since we started watching (first checked Aug 13, 2026, 9:03 PM).
10 CVEs have an estimated 10%-or-higher chance of having already been exploited despite not appearing on CISA's KEV catalog. KEV is a curated record of confirmed cases rather than a complete census, so this is where its coverage is likely thinnest — an estimate from EPSS history, not a finding. Based on a median of 2 EPSS observations per CVE.
Likely-exploited estimates here rest on a median of 2 EPSS observations per CVE — too little history to read as a trend yet. It deepens daily as scores are collected.
SQL injection vulnerability in gallery.asp in Absolute Image Gallery 2.0 allows remote attackers to execute arbitrary SQL commands via the categoryid parameter in a viewimage action.
Multiple absolute path traversal vulnerabilities in Fantastico, as used with cPanel 10.x, allow remote authenticated users to include and execute arbitrary local files via (1) the userlanguage paramet…
Not a quality rating or endorsement — a measure of how much verified, disclosed data we actually have about this vendor. A low score usually means "we don't have much verified information yet," not "this is a bad vendor." Never used to sort or rank vendor lists.
The platform admin controls the formula's weights.
Product information on this page is auto-generated by 0-Doubt from public sources and not yet confirmed by the vendor or an independent analyst, unless an item is individually labelled otherwise. How trust works →
What do they do when something goes wrong?
What their public record shows about handling vulnerabilities and outages.
Do they tell you the awkward things unprompted?
How much this vendor volunteers before you have to ask.
Are they still shipping, or coasting?
Whether this vendor is visibly still building.
Nothing checked here yet — this is not a mark against Absolute.
Infrastructure & transparency signals
Stack-based buffer overflow in the NCTAudioFile2.AudioFile ActiveX control (NCTAudioFile2.dll), as used by multiple products, allows remote attackers to execute…
Microsoft Internet Explorer 6 and earlier allows remote attackers to obtain sensitive information via unspecified uses of the OBJECT HTML tag, which discloses t…
Directory traversal vulnerability in Oracle Reports 6.0, 6i, 9i, and 10g allows remote attackers to overwrite arbitrary files via (1) "..", (2) Windows drive le…
Multiple directory traversal vulnerabilities in Sambar Server 6.1 Beta 2 on Windows, and possibly other versions on Linux, when the administrative IP address re…
Directory traversal vulnerability in Oracle Reports allows remote attackers to read arbitrary files via an absolute or relative path to the (1) CUSTOMIZE or (2)…
Absolute path traversal vulnerability in Oracle Database Server, when utl_file_dir is set to a wildcard value or "CREATE ANY DIRECTORY to PUBLIC" privileges exist, allows remote authenticated users to…
Directory traversal vulnerability in upload/bin/download.php in Upload Tool for PHP 1.0 allows remote attackers to read arbitrary files via (1) ".." sequences or (2) absolute pathnames in the filename…
Absolute path traversal vulnerability in list_main_pages.php in Cromosoft Simple Plantilla PHP (SPP) allows remote attackers to list arbitrary directories, and read arbitrary files, via an absolute pa…
Directory traversal vulnerability in index.php in Jupiter CMS 1.1.5 allows remote attackers to include and execute arbitrary local files via a .. (dot dot), or an absolute pathname, in the n parameter…
PGP Desktop before 9.5.1 does not validate data objects received over the (1) \pipe\pgpserv named pipe for PGPServ.exe or the (2) \pipe\pgpsdkserv named pipe for PGPsdkServ.exe, which allows remote au…
Stack-based buffer overflow in the NCTAudioFile2.AudioFile ActiveX control (NCTAudioFile2.dll), as used by multiple products, allows remote attackers to execute arbitrary code via a long argument to t…
Multiple absolute path traversal vulnerabilities in EditTag 1.2 allow remote attackers to read arbitrary files via an absolute pathname in the file parameter to (1) edittag.cgi, (2) edittag.pl, (3) ed…
Microsoft Internet Explorer 6 and earlier allows remote attackers to obtain sensitive information via unspecified uses of the OBJECT HTML tag, which discloses the absolute path of the corresponding TI…
Absolute path traversal vulnerability in abitwhizzy.php before 20061204 allows remote attackers to read arbitrary files via an absolute pathname in the Filename text window (f parameter), a variant of…
Directory traversal vulnerability in download.php in Sisfo Kampus 0.8 allows remote attackers to list arbitrary directories via an absolute pathname in the dir parameter.
Directory traversal vulnerability in textview.php in Anton Vlasov DoSePa 1.0.4 allows remote attackers to read arbitrary files via a .. (dot dot) sequence or absolute file path in the file parameter.
Absolute path traversal vulnerability in admin/logfile.txt in Verity Ultraseek before 5.6.2 allows remote attackers to read arbitrary files via the name variable.
Heap-based buffer overflow in FutureSoft TFTP Server Multithreaded (MT) 1.1 allows remote attackers to cause a denial of service (crash) or possibly execute arbitrary code by sending a crafted packet …
Absolute path traversal vulnerability in includes/functions_portal.php in IntegraMOD Portal 2.x and earlier, when magic_quotes_gpc is disabled, allows remote attackers to read arbitrary files via an a…
Absolute path traversal vulnerability in the get functionality in Anti-Spam SMTP Proxy (ASSP) allows remote authenticated users to read arbitrary files via (1) C:\ (Windows drive letter), (2) UNC, and…
Absolute path traversal vulnerability in downloadTrigger.jsp in Alkacon OpenCms before 6.2.2 allows remote authenticated users to download arbitrary files via an absolute pathname in the filePath para…
Absolute path directory traversal vulnerability in (a) MERAK Mail Server for Windows 8.3.8r with before IceWarp Web Mail 5.6.1 and (b) VisNetic MailServer before 8.5.0.5 allows remote attackers to inc…
Absolute path directory traversal vulnerability in (1) MERAK Mail Server for Windows 8.3.8r with before IceWarp Web Mail 5.6.1 and (2) VisNetic MailServer before 8.5.0.5 allows remote authenticated us…
Absolute path traversal vulnerability in administrador.asp in VirtuaStore 2.0 allows remote attackers to possibly read arbitrary directories or files via an absolute path with Windows drive letter in …
Absolute path traversal vulnerability in the copy action in index.php in Andrew Godwin ByteHoard 2.1 and earlier allows remote authenticated users to create or overwrite files in other users' director…
Directory traversal vulnerability in webcm in the D-Link DSL-G604T Wireless ADSL Router Modem allows remote attackers to read arbitrary files via an absolute path in the getpage parameter.
Directory traversal vulnerability in Dynamic Galerie 1.0 allows remote attackers to access arbitrary files via an absolute path in the pfad parameter to (1) index.php and (2) galerie.php.
Absolute path traversal vulnerability in index.php in 321soft PhP-Gallery 0.9 allows remote attackers to browse arbitrary directories via the path parameter.
Absolute path traversal vulnerability in recordings/misc/audio.php in the Asterisk Recording Interface (ARI) web interface in Asterisk@Home before 2.8 allows remote attackers to read arbitrary MP3, WA…
Directory traversal vulnerability in admin/folders/saveuploadfiles.asp in Hosting Controller 2002 RC 1 allows remote authenticated users to overwrite arbitrary files via an absolute path in the OpenPa…
Cross-site scripting (XSS) vulnerability in afmsearch.aspx in Absolute FAQ Manager .NET 4.0 and earlier allows remote attackers to inject arbitrary web script or HTML via unspecified search module par…
Multiple cross-site scripting (XSS) vulnerabilities in XIGLA Absolute Live Support XE 2.0 and earlier allow remote attackers to inject arbitrary web script or HTML via the (1) Screen name or (2) Sessi…
Cross-site scripting (XSS) vulnerability in Absolute Image Gallery XE 2.0 and earlier allows remote attackers to inject arbitrary web script or HTML via (1) the shownew parameter in gallery.asp and (2…
Absolute path traversal vulnerability in Easy File Sharing (EFS) Web Server 3.2 allows remote registered users to execute arbitrary code by uploading a malicious file to the Windows startup folder.
CubeCart 3.0 through 3.6 does not properly check authorization for an administration session because of a missing auth.inc.php include, which results in an absolute path traversal vulnerability in Fil…
Absolute path traversal vulnerability in docs/showdocs.php in Coppermine Photo Gallery 1.4.3 and earlier allows remote attackers to include arbitrary files via the f parameter, and possibly remote fil…
Multiple unspecified vulnerabilities in lib-common.php in Geeklog 1.4.0 before 1.4.0sr1 and 1.3.11 before 1.3.11sr4 allow remote attackers to include arbitrary local files and execute arbitrary code v…
Absolute path traversal vulnerability in convert.cgi in Quirex 2.0.2 and earlier allows remote attackers to read arbitrary files, and possibly execute arbitrary code, via the (1) quiz_head, (2) quiz_f…
Absolute path traversal vulnerability in include.php in PHPKIT 1.6.1 Release 2 and earlier allows remote attackers to include and execute arbitrary local files via a direct request with a path paramet…
WmRoot/adapter-index.dsp in SAP Business Connector Core Fix 7 and earlier allows remote attackers to conduct spoofing (phishing) attacks via an absolute URL in the url parameter, which loads the URL i…
Cross-site scripting (XSS) vulnerability in Absolute Image Gallery XE 2.x allows remote attackers to inject arbitrary web script or HTML via the text parameter. NOTE: the provenance of this informati…
Multiple SQL injection vulnerabilities in Absolute Shopping Package Solutions (ASPS) Shopping Cart Professional 2.9d and earlier, and Lite 2.1 and earlier, allow remote attackers to execute arbitrary …
Exponent CMS 0.96.3 and later versions includes the full installation path in the base parameter to thumb.php, which allows remote attackers to obtain sensitive information. NOTE: this might be resul…
Absolute path traversal vulnerability in Rockliffe MailSite Express before 6.1.22 allows remote attackers to read arbitrary files via a full pathname in the AttachPath field of a mail message under co…
Directory traversal vulnerability in a third-party compression library (UNACEV2.DLL), as used in avast! Antivirus Home/Professional Edition 4.6.665 and Server Edition 4.6.460, allows remote attackers …
Directory traversal vulnerability in Oracle Reports allows remote attackers to read arbitrary files via an absolute or relative path to the (1) CUSTOMIZE or (2) desformat parameters to rwservlet. NOT…
Oracle Forms 4.5 through 10g starts form executables from arbitrary directories and executes them as the Oracle or System user, which allows attackers to execute arbitrary code by uploading a maliciou…
Directory traversal vulnerability in Oracle Reports 6.0, 6i, 9i, and 10g allows remote attackers to overwrite arbitrary files via (1) "..", (2) Windows drive letter (C:), and (3) absolute path sequenc…
Golden FTP Server Pro 2.52 allows remote attackers to obtain sensitive information via a GET request for a file that does not exist, which reveals the absolute path of the FTP server in the resulting …
Multiple directory traversal vulnerabilities in unace 1.2b allow attackers to overwrite arbitrary files via an ACE archive containing (1) ../ sequences or (2) absolute pathnames.
The Management Agent in F-Secure Policy Manager 5.11.2810 allows remote attackers to gain sensitive information, such as the absolute path for the web server, via an HTTP request to fsmsh.dll without …
Multiple directory traversal vulnerabilities in Sambar Server 6.1 Beta 2 on Windows, and possibly other versions on Linux, when the administrative IP address restrictions have been modified from the d…
Directory traversal vulnerability in lstat.cgi in LinuxStat before 2.3.1 allows remote attackers to read arbitrary files via (1) .. (dot dot) sequences or (2) absolute paths to the template parameter.
Absolute path traversal vulnerability in Quake II server before R1Q2 on Linux, as used in multiple products, allows remote attackers to cause a denial of service (application crash) via a download com…
Absolute path traversal vulnerability in Quake II server before R1Q2 on Windows, as used in multiple products, allows remote attackers to read arbitrary files via a "\/" in a pathname argument, as dem…
Absolute path traversal vulnerability in main.cgi in Linksys WVC11B Wireless-B Internet Video Camera allows remote attackers to read arbitrary files via an absolute pathname in the next_file parameter…
OWLS 1.0 allows remote attackers to retrieve arbitrary files via absolute pathnames in (1) the file parameter in /glossaries/index.php, (2) the filename parameter in /readings/index.php, or (3) the fi…
WFTPD Pro Server 3.21 Release 1, with the XeroxDocutech option enabled, allows local users to cause a denial of service (crash) via a (1) MKD or (2) XMKD command that causes an absolute path of 260 ch…
The unix_clean_name function in Samba 2.2.x through 2.2.11, and 3.0.x before 3.0.2a, trims certain directory names down to absolute paths, which could allow remote attackers to bypass the specified sh…
Multiple directory traversal vulnerabilities in LHA 1.14 allow remote attackers or local users to create arbitrary files via an LHA archive containing filenames with (1) .. sequences or (2) absolute p…
ISQL*Plus in Oracle 10g Application Server allows remote attackers to execute arbitrary files via an absolute pathname in the file parameter to the load.uix script.
The client for CVS before 1.11 allows a remote malicious CVS server to create arbitrary files using certain RCS diff files that use absolute pathnames during checkouts or updates, a different vulnerab…
phpGedView before 2.65 allows remote attackers to obtain the absolute path of the web server via malformed parameters to (1) indilist.php, (2) famlist.php, (3) placelist.php, (4) imageview.php, (5) ti…
Absolute path traversal vulnerability in Alt-N Technologies WebAdmin 2.0.0 through 2.0.2 allows remote attackers with administrator privileges to (1) determine the installation path by reading the con…
Absolute path traversal vulnerability in nukestyles.com viewpage.php addon for PHP-Nuke allows remote attackers to read arbitrary files via a full pathname in the file parameter. NOTE: This was origi…
MyWebServer 1.0.2 allows remote attackers to determine the absolute path of the web document root via a request for a directory that does not exist, which leaks the pathname in an error message.
tmp_view.php in FUDforum before 2.2.0 allows remote attackers to read arbitrary files via an absolute pathname in the file parameter.
Directory traversal vulnerability in ASTAware SearchDisk engine for Sun ONE Starter Kit 2.0 allows remote attackers to read arbitrary files via a .. (dot dot) attack on port (1) 6015 or (2) 6016, or (…
bonsai Mozilla CVS query tool leaks the absolute pathname of the tool in certain error messages generated by (1) cvslog.cgi, (2) cvsview2.cgi, or (3) multidiff.cgi.
CooolSoft Personal FTP Server 2.24 allows remote attackers to obtain the absolute pathname of the FTP root via a PWD command, which includes the full path in the response.
The installation procedure for Invision Board suggests that users install the phpinfo.php program under the web root, which leaks sensitive information such as absolute pathnames, OS information, and …
SquirrelMail 1.2.7 and earlier allows remote attackers to determine the absolute pathname of the options.php script via a malformed optpage file argument, which generates an error message when the fil…
none.php for SunPS iRunbook 2.5.2 allows remote attackers to read arbitrary files via an absolute pathname in the argument.
ASP-Nuke RC2 and earlier allows remote attackers to determine the absolute path of the server by (1) calling database-inc.asp with incorrect cookies, or (2) calling Post.asp with certain arguments, wh…
bigsam_guestbook.php for Big Sam (Built-In Guestbook Stand-Alone Module) 1.1.08 and earlier allows remote attackers to cause a denial of service (CPU consumption) or obtain the absolute path of the we…
categorie.php3 in Black Tie Project (BTP) 0.4b through 0.5b allows remote attackers to determine the absolute path of the web server via an invalid category ID (cid) parameter, which leaks the pathnam…
ColdFusion 5.0 and earlier on Windows systems allows remote attackers to determine the absolute pathname of .cfm or .dbm files via an HTTP request that contains an MS-DOS device name such as NUL, whic…
Citrix Nfuse 1.51 allows remote attackers to obtain the absolute path of the web root via a malformed request to launch.asp that does not provide the session field.
Internet Software Solutions Air Messenger LAN Server (AMLServer) 3.4.2 allows remote attackers to obtain an absolute path for the server directory by viewing the Location header.
Xcache 2.1 allows remote attackers to determine the absolute path of web server documents by requesting a URL that is not cached by Xcache, which returns the full pathname in the Content-PageName head…
Muscat Empower CGI program allows remote attackers to obtain the absolute pathname of the server via an invalid request in the DB parameter.
Unspecified vulnerability in siteman.php3 in AnyPortal(php) before 22 APR 00 allows remote attackers to obtain sensitive information via unknown attack vectors, which reveal the absolute path. NOTE: …
Eudora mail client includes the absolute path of the sender's host within a virtual card (VCF).
Tnef program in Linux systems allows remote attackers to overwrite arbitrary files via TNEF encoded compressed attachments which specify absolute path names for the decompressed output.
Net Tools PKI Server does not properly restrict access to remote attackers when the XUDA template files do not contain absolute pathnames for other files.
Falcon web server allows remote attackers to determine the absolute path of the web root via long file names.