Represented by Carahsoft ↗, Exclusive Networks ↗, World Wide Technology ↗, ePlus ↗
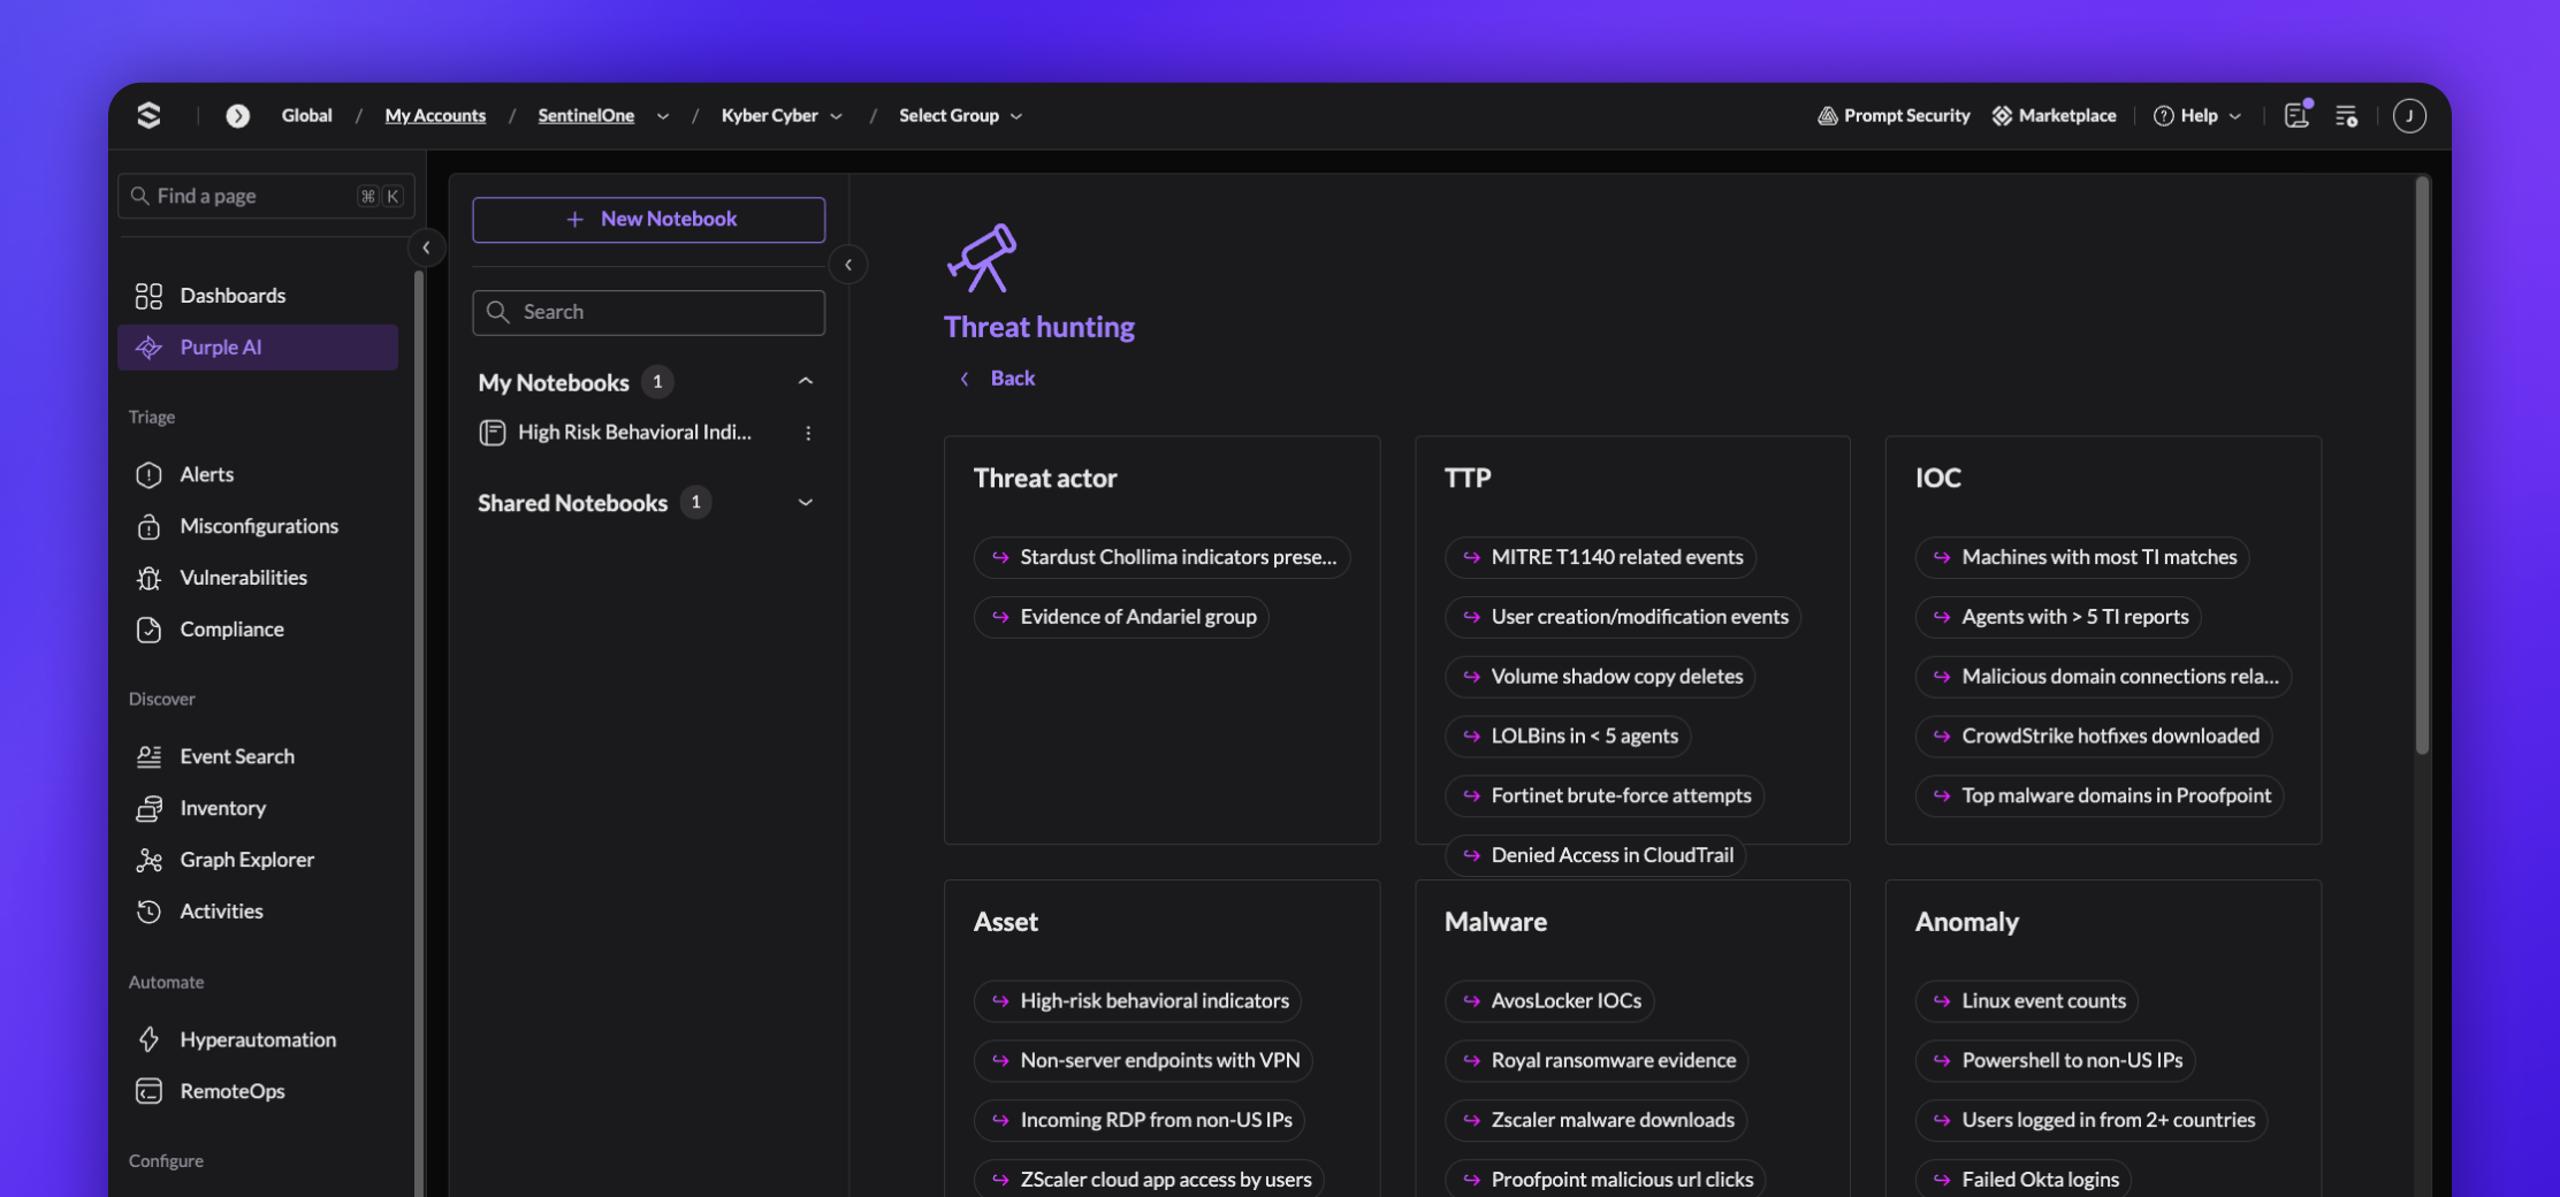
Autonomous endpoint protection and XDR platform.
Tools & products
Read by an AI model from sentinelone.com’s own pages. What the vendor says it does, not independently verified.
Drawn from this vendor's own public materials and authored to keep category questionnaires balanced. Gaps reflect capabilities not emphasized in public materials, not rankings.
Strengths: Autonomous on-agent prevention and response with ransomware rollback and native XDR across endpoint, cloud, and identity.
Gaps: Public materials emphasize automation; depth of fully-managed (analyst-led) response is detailed less than the self-driving capabilities.
Integrates with: Arctic Wolf ↗, Armis ↗, Autonomous Security ↗, Broadcom ↗, Cybereason ↗, Exabeam ↗, Google ↗, Magic ↗, Microsoft ↗, Mimecast ↗, N-able ↗, Native Security ↗, Netskope ↗, NinjaOne ↗, Palo Alto Networks ↗, Ping Identity ↗, Prompt Security ↗, Proofpoint ↗, Recorded Future ↗, ReversingLabs ↗, ServiceNow ↗, Sophos ↗, Splunk ↗, Threat Intelligence ↗, Trellix ↗, Trend Micro ↗, Zscaler ↗
Integrated by: 1Kosmos, 1stProtect.ai, ANY.RUN, Above Security, Abstract Security, Acronis International GmbH, AiStrike, Amplifier Security, Andesite, Anvilogic, Beyond Identity, Binalyze, Blackpoint Cyber, Blink Ops, BullWall, Cisco, Claroty, Cloudflare, Coalition, Cogent Security, ColorTokens Inc., Comodo, Complyan, Complyance, Compyl
2 of 5 independent trust signals established
SentinelOne has 2 dimensions with established evidence. The rest have not been confirmed yet.
Not yet established: Independently verified · Behaviour under stress · Disclosure posture
Has anyone other than the vendor confirmed this?
1 independent source(s) corroborate this vendor's claims.
Is this a real, durable business?
How long this vendor has been operating, and who stands behind them.
What do they do when something goes wrong?
What their public record shows about handling vulnerabilities and outages.
Do they tell you the awkward things unprompted?
How much this vendor volunteers before you have to ask.
Are they still shipping, or coasting?
Whether this vendor is visibly still building.
Certifications & compliance claimsWhat the tiers meanVerified in a public registry — we confirmed this against an authoritative public registry (FedRAMP Marketplace, CSA STAR) and re-check it by the registry's own identifier. Stated by the vendor — the vendor says it on a page they control; a sourced claim about themselves, not an independent check. Detected on a page — found during automated enrichment, neither registry-confirmed nor stated on the vendor's own site.
Some certifications have no public registry at all — SOC 2 and HIPAA among them. For those, “not registry-verified” is not a shortfall and means nothing about the vendor.
Stated by the vendor
Some of these (SOC 2, HIPAA and similar) have no public registry, so no one can independently verify them — that is a fact about the framework, not about this vendor.
Security headers (5/5) — checked 10/18/2026
Infrastructure & transparency signals
No outages recorded since we started watching (first checked Aug 13, 2026, 8:30 PM).
Not a quality rating or endorsement — a measure of how much verified, disclosed data we actually have about this vendor. A low score usually means "we don't have much verified information yet," not "this is a bad vendor." Never used to sort or rank vendor lists.
The platform admin controls the formula's weights.
Datasheets, whitepapers, and case studies found on sentinelone.com by the enrichment loop. Links open the original documents on the vendor's own site.
Product information on this page is auto-generated by 0-Doubt from public sources and not yet confirmed by the vendor or an independent analyst, unless an item is individually labelled otherwise. How trust works →