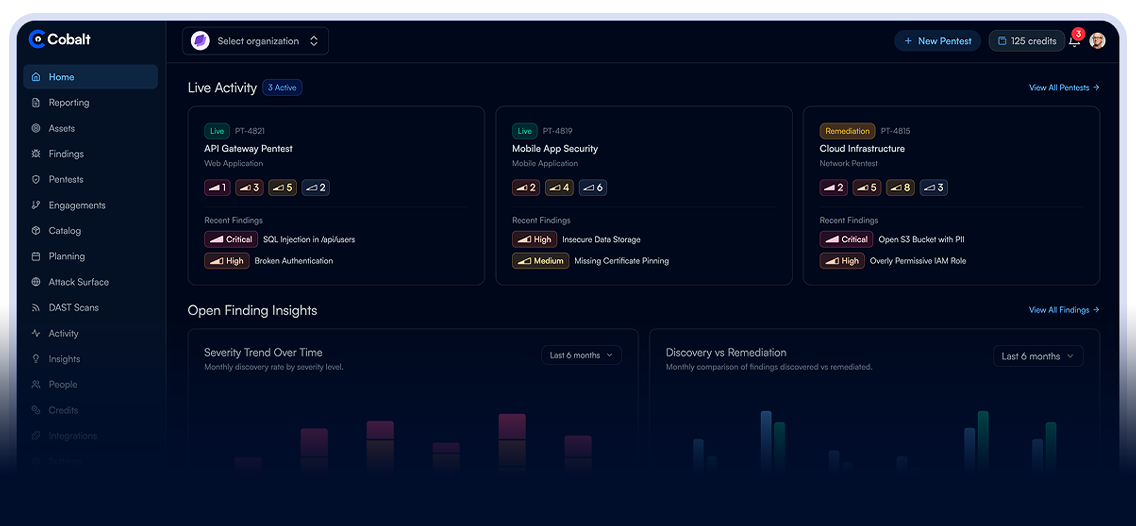
Continuous external asset discovery and monitoring with daily domain scans. AI-generated from public sourcesThe starting point for every profile: auto-generated by 0-Doubt from public vendor materials, and not yet confirmed by the vendor or an independent analyst. Nothing here is hidden or overstated — it simply has not been reviewed yet.Where every profile starts, before the vendor or an analyst has reviewed it. A higher label means a more independent source — not a better product.How trust works →
Tools & products
Read by an AI model from cobalt.io’s own pages. What the vendor says it does, not independently verified.
Showing the 12 closest of 14 — see all.
Integrates with: Embed Security ↗, Microsoft ↗, ServiceNow ↗
Integrated by: Core Security, DevOcean, Faradaysec, Pentera, PlexTrac, Red Canary, Seemplicity, Trent AI, UncommonX, Zeguro, processgene
1 of 5 independent trust signals established
Cobalt has one dimension with established evidence. The rest have not been confirmed yet.
Not yet established: Independently verified · Operating durability · Disclosure posture · Momentum
Has anyone other than the vendor confirmed this?
Nothing here has been confirmed by an independent third party yet.
Is this a real, durable business?
How long this vendor has been operating, and who stands behind them.
Security headers (5/5) — checked 10/18/2026
Infrastructure & transparency signals
Likely-exploited estimates here rest on a median of 2 EPSS observations per CVE — too little history to read as a trend yet. It deepens daily as scores are collected.
Ashlar-Vellum Cobalt CO File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Ve…
Ashlar-Vellum Cobalt CO File Parsing Type Confusion Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vellum…
Not a quality rating or endorsement — a measure of how much verified, disclosed data we actually have about this vendor. A low score usually means "we don't have much verified information yet," not "this is a bad vendor." Never used to sort or rank vendor lists.
The platform admin controls the formula's weights.
Product information on this page is auto-generated by 0-Doubt from public sources and not yet confirmed by the vendor or an independent analyst, unless an item is individually labelled otherwise. How trust works →
What do they do when something goes wrong?
What their public record shows about handling vulnerabilities and outages.
Do they tell you the awkward things unprompted?
How much this vendor volunteers before you have to ask.
Are they still shipping, or coasting?
Whether this vendor is visibly still building.
Cobalt Strike 4.7.1 fails to properly escape HTML tags when they are displayed on Swing components. By injecting crafted HTML code, it is possible to remotely e…
An XSS (Cross Site Scripting) vulnerability was found in HelpSystems Cobalt Strike through 4.7 that allowed a remote attacker to execute HTML on the Cobalt Stri…
overflow.cgi CGI script in Sun Cobalt RaQ 4 with the SHP (Security Hardening Patch) installed allows remote attackers to execute arbitrary code via a POST reque…
Directory traversal vulnerability in readmsg.php in WebMail 2.0.1 in Cobalt Qube 3 allows remote attackers to read arbitrary files via a .. (dot dot) in the mai…
The default configuration of Cobalt RaQ2 and RaQ3 as specified in access.conf allows remote attackers to view sensitive contents of a .htaccess file.
Ashlar-Vellum Cobalt CO File Parsing Memory Corruption Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vel…
Ashlar-Vellum Cobalt LI File Parsing Type Confusion Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vellum…
Ashlar-Vellum Cobalt AR File Parsing Type Confusion Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vellum…
Ashlar-Vellum Cobalt CO File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-V…
Ashlar-Vellum Cobalt XE File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Ve…
Ashlar-Vellum Cobalt AR File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-V…
Ashlar-Vellum Cobalt CO File Parsing Type Confusion Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vellum…
Ashlar-Vellum Cobalt AR File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Ve…
Ashlar-Vellum Cobalt LI File Parsing Use-After-Free Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vellum…
Ashlar-Vellum Cobalt AR File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Ve…
Ashlar-Vellum Cobalt VC6 File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-V…
Ashlar-Vellum Cobalt VC6 File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-…
Ashlar-Vellum Cobalt AR File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Ve…
Ashlar-Vellum Cobalt VC6 File Parsing Integer Overflow Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vel…
Ashlar-Vellum Cobalt AR File Parsing Uninitialized Variable Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashla…
Ashlar-Vellum Cobalt LI File Parsing Integer Overflow Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Vell…
Ashlar-Vellum Cobalt LI File Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ashlar-Ve…
In Ashlar-Vellum Cobalt, Xenon, Argon, Lithium, and Cobalt Share versions prior to 12.6.1204.204, the affected applications lack proper validation of user-supplied data when parsing XE files. This cou…