IT productivity & security suite: PAM, remote access, and password mgmt. AI-generated from public sourcesThe starting point for every profile: auto-generated by 0-Doubt from public vendor materials, and not yet confirmed by the vendor or an independent analyst. Nothing here is hidden or overstated — it simply has not been reviewed yet.Where every profile starts, before the vendor or an analyst has reviewed it. A higher label means a more independent source — not a better product.How trust works →
Tools & products
We build profiles from public sources and haven't extracted a capability list for Devolutions. Closest sources we do hold:
Showing the 12 closest of 264 — see all.
Integrates with: 1Password ↗, Bastion ↗, BeyondTrust ↗, Bitwarden ↗, Cerby ↗, CyberArk ↗, Delinea ↗, Google ↗
4 of 5 independent trust signals established
Devolutions has 4 dimensions with established evidence. The rest have not been confirmed yet.
Not yet established: Independently verified
Has anyone other than the vendor confirmed this?
1 independent source(s) corroborate this vendor's claims.
Is this a real, durable business?
How long this vendor has been operating, and who stands behind them.
Certifications & compliance claimsWhat the tiers meanVerified in a public registry — we confirmed this against an authoritative public registry (FedRAMP Marketplace, CSA STAR) and re-check it by the registry's own identifier. Stated by the vendor — the vendor says it on a page they control; a sourced claim about themselves, not an independent check. Detected on a page — found during automated enrichment, neither registry-confirmed nor stated on the vendor's own site.
Some certifications have no public registry at all — SOC 2 and HIPAA among them. For those, “not registry-verified” is not a shortfall and means nothing about the vendor.
Detected on a page
Security headers (3/5) — checked 10/18/2026
No outages recorded since we started watching (first checked Aug 14, 2026, 12:17 AM).
7 CVEs have an estimated 10%-or-higher chance of having already been exploited despite not appearing on CISA's KEV catalog. KEV is a curated record of confirmed cases rather than a complete census, so this is where its coverage is likely thinnest — an estimate from EPSS history, not a finding. Based on a median of 2 EPSS observations per CVE.
Likely-exploited estimates here rest on a median of 2 EPSS observations per CVE — too little history to read as a trend yet. It deepens daily as scores are collected.
Improper access control in secure message component in Devolutions Server allows an authenticated user to steal unauthorized entries via the secure message entry attachment feature This issue affect…
Use of weak credentials in emergency authentication component in Devolutions Server allows an unauthenticated attacker to bypass authentication via brute forcing the short emergency codes generated by…
Not a quality rating or endorsement — a measure of how much verified, disclosed data we actually have about this vendor. A low score usually means "we don't have much verified information yet," not "this is a bad vendor." Never used to sort or rank vendor lists.
The platform admin controls the formula's weights.
Product information on this page is auto-generated by 0-Doubt from public sources and not yet confirmed by the vendor or an independent analyst, unless an item is individually labelled otherwise. How trust works →
What do they do when something goes wrong?
What their public record shows about handling vulnerabilities and outages.
Do they tell you the awkward things unprompted?
How much this vendor volunteers before you have to ask.
Are they still shipping, or coasting?
Whether this vendor is visibly still building.
Infrastructure & transparency signals
An incomplete permission check on entries in Devolutions Remote Desktop Manager before 2021.2.16 allows attackers to bypass permissions via batch custom PowerSh…
A path traversal issue in entry attachments in Devolutions Remote Desktop Manager before 2022.2 allows attackers to create or overwrite files in an arbitrary lo…
An issue was discovered in Devolutions Remote Desktop Manager before 2020.2.12. There is a cross-site scripting (XSS) vulnerability in webviews.
Cross-Site Scripting (XSS) in Administrative Reports in Devolutions Remote Desktop Manager before 2021.1 allows remote authenticated users to inject arbitrary w…
An issue was discovered in Devolutions Server before 2020.3. There is an exposure of sensitive information in diagnostic files.
Improper access control in users MFA feature in Devolutions Server 2025.1.7.0 and earlier allows a user with user management permission to remove or change administrators MFA.
Improper access control in Tor network blocking feature in Devolutions Server 2025.1.10.0 and earlier allows an authenticated user to bypass the tor blocking feature when the Devolutions hosted endpoi…
Improper access control in permissions component in Devolutions Server 2025.1.10.0 and earlier allows an authenticated user to bypass the "Edit permission" permission by bypassing the client side vali…
Improper access control in user group management in Devolutions Server 2025.1.7.0 and earlier allows a non-administrative user with both "User Management" and "User Group Management" permissions to pe…
Exposure of private personal information to an unauthorized actor in the user vaults component of Devolutions Remote Desktop Manager allows an authenticated user to gain unauthorized access to private…
Improper privilege assignment in PAM JIT privilege sets in Devolutions Server allows a PAM user to perform PAM JIT requests on unauthorized groups by exploiting a user interface issue. This issue …
Improper access control in PAM feature in Devolutions Server allows a PAM user to self approve their PAM requests even if disallowed by the configured policy via specific user interface actions. …
Incorrect privilege assignment in PAM JIT elevation feature in Devolutions Server 2025.1.5.0 and earlier allows a PAM user to elevate a previously configured user configured in a PAM JIT account via f…
Improper authorization in the variable component in Devolutions Remote Desktop Manager on Windows allows an authenticated user to use the ELEVATED_PASSWORD variable even though not allowed by the "All…
Insufficient logging in the autotyping feature in Devolutions Remote Desktop Manager on Windows allows an authenticated user to use a stored password without generating a corresponding log event, via …
Improper authorization in application password policy in Devolutions Remote Desktop Manager on Windows allows an authenticated user to use a configuration different from the one mandated by the syste…
Client side access control bypass in the permission component in Devolutions Remote Desktop Manager on Windows. An authenticated user can exploit this flaw to bypass certain permission restrictions—s…
Improper access control in web extension restriction feature in Devolutions Server 2024.3.4.0 and earlier allows an authenticated user to bypass the browser extension restriction feature.
Improper access control in temporary access requests and checkout requests endpoints in Devolutions Server 2024.3.13 and earlier allows an authenticated user to access information about these requests…
Exposure of password in web-based SSH authentication component in Devolutions Server 2024.3.13 and earlier allows a user to unadvertently leak his SSH password due to missing password masking.
Exposure of sensitive information in My Personal Credentials password history component in Devolutions Remote Desktop Manager 2024.3.29 and earlier on Windows allows an authenticated user to inadverte…
Exposure of sensitive information in hub data source export feature in Devolutions Remote Desktop Manager 2024.3.29 and earlier on Windows allows a user exporting a hub data source to include his auth…
Incorrect authorization in PAM vaults in Devolutions Server 2024.3.12 and earlier allows an authenticated user to bypass the 'add in root' permission.
Improper password reset in PAM Module in Devolutions Server 2024.3.10.0 and earlier allows an authenticated user to reuse the oracle user password after check-in due to crash in the password reset fun…
Improper host validation in the certificate validation component in Devolutions Remote Desktop Manager on 2024.3.19 and earlier on Windows allows an attacker to intercept and modify encrypted communic…
Missing certificate validation in Devolutions Remote Desktop Manager on macOS, iOS, Android, Linux allows an attacker to intercept and modify encrypted communications via a man-in-the-middle attack. …
Incorrect authorization in the permission component in Devolutions Server 2024.3.7.0 and earlier allows an authenticated user to view the password history of an entry without the view password permiss…
Incorrect permission assignment in the user migration feature in Devolutions Server 2024.3.8.0 and earlier allows users to retain their old permission sets.
Incorrect permission assignment in temporary access requests component in Devolutions Remote Desktop Manager 2024.3.19.0 and earlier on Windows allows an authenticated user that request temporary perm…
Incorrect authorization in permission validation component in Devolutions Server 2024.3.6.0 and earlier allows an authenticated user to access some reporting endpoints.
Non constant time cryptographic operation in Devolutions.XTS.NET 2024.11.19 and earlier allows an attacker to render half of the encryption key obsolete via a timing attacks
Incorrect authorization in the add permission component in Devolutions Remote Desktop Manager 2024.2.21 and earlier on Windows allows an authenticated malicious user to bypass the "Add" permission via…
Improper authentication in SQL data source MFA validation in Devolutions Remote Desktop Manager 2024.3.17 and earlier on Windows allows an authenticated user to bypass the MFA validation via data sour…
Incorrect authorization in the permission validation component of Devolutions Remote Desktop Manager 2024.2.21 and earlier on Windows allows a malicious authenticated user to bypass the "View Password…
Improper access control in the Password History feature in Devolutions DVLS 2024.3.6 and earlier allows a malicious authenticated user to obtain sensitive data via faulty permission.
An information exposure in Devolutions Remote Desktop Manager 2024.2.20.0 and earlier on Windows allows local attackers with access to system logs to obtain session credentials via passwords included …
Authorization bypass in the PAM access request approval mechanism in Devolutions Server 2024.2.10 and earlier allows authenticated users with permissions to approve their own requests, bypassing inten…
Exposure of Sensitive Information in edge browser session proxy feature in Devolutions Remote Desktop Manager 2024.2.14.0 and earlier on Windows allows an attacker to intercept proxy credentials via a…
Improper access control in PAM dashboard in Devolutions Remote Desktop Manager 2024.2.11 and earlier on Windows allows an authenticated user to bypass the execute permission via the use of the PAM das…
Authentication bypass in the 2FA feature in Devolutions Server 2024.1.14.0 and earlier allows an authenticated attacker to authenticate to another user without being asked for the 2FA via another brow…
Improper authentication in the vault password feature in Devolutions Remote Desktop Manager 2024.1.31.0 and earlier allows an attacker that has compromised an access to an RDM instance to bypass the v…
Improper removal of sensitive information in data source export feature in Devolutions Remote Desktop Manager 2024.1.32.0 and earlier on Windows allows an attacker that obtains the exported settings t…
Improper input validation in PAM JIT elevation feature in Devolutions Server 2024.1.11.0 and earlier allows an authenticated user with access to the PAM JIT elevation feature to manipulate the LDAP fi…
Improper permission handling in the vault offline cache feature in Devolutions Remote Desktop Manager 2024.1.20 and earlier on windows and Devolutions Server 2024.1.8 and earlier allows an attacker to…
Improper input validation in PAM JIT elevation feature in Devolutions Server 2024.1.6 and earlier allows an attacker with access to the PAM JIT elevation feature to forge the displayed group in the PA…
Improper access control in PAM vault permissions in Devolutions Server 2024.1.10.0 and earlier allows an authenticated user with access to the PAM to access unauthorized PAM entries via a specific set…
Improper access control in PAM JIT elevation in Devolutions Server 2024.1.6 and earlier allows an attacker with access to the PAM JIT elevation feature to elevate themselves to unauthorized groups via…
Improper cleanup in temporary file handling component in Devolutions Remote Desktop Manager 2024.1.12 and earlier on Windows allows an attacker that compromised a user endpoint, under specific circum…
Improper access control in the user interface in Devolutions Workspace 2024.1.0 and earlier allows an authenticated user to perform unintended actions via specific permissions
Denial of service in PAM password rotation during the check-in process in Devolutions Server 2023.3.14.0 allows an authenticated user with specific PAM permissions to make PAM credentials unavailable.…
Improper session management in the identity provider authentication flow in Devolutions Server 2023.3.14.0 and earlier allows an authenticated user via an identity provider to stay authenticated after…
Improper access control in the notification feature in Devolutions Server 2023.3.14.0 and earlier allows a low privileged user to change notifications settings configured by an administrator.
Improper privilege management in Just-in-time (JIT) elevation module in Devolutions Server 2023.3.14.0 and earlier allows a user to continue using the elevated privilege even after the expiration unde…
Cross-site scripting (XSS) vulnerability in the entry overview tab in Devolutions Remote Desktop Manager 2023.3.36 and earlier on Windows allows an attacker with access to a data source to inject a ma…
Inadequate validation of permissions when employing remote tools and macros via the context menu within Devolutions Remote Desktop Manager versions 2023.3.31 and earlier permits a user to initiate …
Client side permission bypass in Devolutions Remote Desktop Manager 2023.3.4.0 and earlier on iOS allows an attacker that has access to the application to execute entries in a SQL data source withou…
Offline mode is always enabled, even if permission disallows it, in Devolutions Server data source in Devolutions Workspace 2023.3.2.0 and earlier. This allows an attacker with access to the Work…
Information leak in Content-Security-Policy header in Devolutions Server 2023.3.7.0 allows an unauthenticated attacker to list the configured Devolutions Gateways endpoints.
Improper access control in the password analyzer feature in Devolutions Remote Desktop Manager 2023.2.33 and earlier on Windows allows an attacker to bypass permissions via data source switching.
Improper access control in Report log filters feature in Devolutions Server 2023.2.10.0 and earlier allows attackers to retrieve logs from vaults or entries they are not allowed to access via the repo…
Improper access control in the permission inheritance in Devolutions Server 2022.3.13.0 and earlier allows an attacker that compromised a low privileged user to access entries via a specific combina…
Improper access control in PAM propagation scripts in Devolutions Server 2023.2.8.0 and ealier allows an attack with permission to manage PAM propagation scripts to retrieve passwords stored in it via…
Improper access controls in the entry duplication component in Devolutions Remote Desktop Manager 2023.2.19 and earlier versions on Windows allows an authenticated user, under specific circumstances, …
Inadequate validation of permissions when employing remote tools and macros within Devolutions Remote Desktop Manager versions 2023.2.19 and earlier permits a user to initiate a connection without pr…
Improper deletion of resource in the user management feature in Devolutions Server 2023.1.8 and earlier allows an administrator to view users vaults of deleted users via database access.
Improper access control in Subscriptions Folder path filter in Devolutions Server 2023.1.1 and earlier allows attackers with administrator privileges to retrieve usage information on folders in user v…
Improper access control in the Web Login listener in Devolutions Remote Desktop Manager 2023.1.22 and earlier on Windows allows an authenticated user to bypass administrator-enforced Web Login restric…
Authentication Bypass in Hub Business integration in Devolutions Workspace Desktop 2023.1.1.3 and earlier on Windows and macOS allows an attacker with access to the user interface to unlock a Hub Bus…
Insufficient access control in support ticket feature in Devolutions Server 2023.1.5.0 and below allows an authenticated attacker to send support tickets and download diagnostic files via specific end…
Two factor authentication bypass on login in Devolutions Remote Desktop Manager 2022.3.35 and earlier allow user to cancel the two factor authentication via the application user interface and open …
No access control for the OTP key on OTP entries in Devolutions Remote Desktop Manager Windows 2022.3.33.0 and prior versions and Remote Desktop Manager Linux 2022.3.2.0 and prior versions allows…
Permission bypass when importing or synchronizing entries in User vault in Devolutions Server 2022.3.13 and prior versions allows users with restricted rights to bypass entry permission via id coll…
Uncontrolled resource consumption in the logging feature in Devolutions Gateway 2023.1.1 and earlier allows an attacker to cause a denial of service by filling up the disk and render the system unusab…
Information disclosure in the user creation feature of a MSSQL data source in Devolutions Remote Desktop Manager 2023.1.9 and below on Windows allows an attacker with access to the user interface to o…
Permission bypass when importing or synchronizing entries in User vault in Devolutions Remote Desktop Manager 2023.1.9 and prior versions allows users with restricted rights to bypass entry permissi…
Improper removal of sensitive data in the entry edit feature of Hub Business submodule in Devolutions Remote Desktop Manager PowerShell Module 2022.3.1.5 and earlier allows an authenticated user to ac…
Improper access control in the secure messages feature in Devolutions Server 2022.3.12 and below allows an authenticated attacker that possesses the message UUID to access the data it contains.
Insufficient input sanitization in the documentation feature of Devolutions Server 2022.3.12 and earlier allows an authenticated attacker to perform an SQL Injection, potentially resulting in unauthor…
Improper access controls on entries in Devolutions Server 2022.3.12 and earlier could allow an authenticated user to access sensitive data without proper authorization.
Improper access controls on some API endpoints in Devolutions Server 2022.3.12 and earlier could allow a standard privileged user to perform privileged actions.
Improper access control in Devolutions Server allows an authenticated user to access unauthorized sensitive data.
The force offline MFA prompt setting is not respected when switching to offline mode in Devolutions Remote Desktop Manager 2022.3.29 to 2022.3.30 allows a user to save sensitive data on disk.
Weak password derivation for export in Devolutions Remote Desktop Manager before 2022.1 allows information disclosure via a password brute-force attack. An error caused base64 to be decoded.
Authentication bypass in local application lock feature in Devolutions Remote Desktop Manager 2022.3.26 and earlier on Windows allows malicious user to access the application.
Elevation of privilege in the Azure SQL Data Source in Devolutions Remote Desktop Manager 2022.3.13 to 2022.3.24 allows an authenticated user to spoof a privileged account.
Dashlane password and Keepass Server password in My Account Settings are not encrypted in the database in Devolutions Remote Desktop Manager 2022.2.26 and prior versions and Devolutions Server 2022.3…
Improper Access Control vulnerability in the Duo SMS two-factor of Devolutions Remote Desktop Manager 2022.2.14 and earlier allows attackers to bypass the application lock. This issue affects: Devolut…
Incorrect permission management in Devolutions Server before 2022.2 allows a new user with a preexisting username to inherit the permissions of that previous user.
HTML injection vulnerability in secure messages of Devolutions Server before 2022.2 allows attackers to alter the rendering of the page or redirect a user to another site.
Information Exposure vulnerability in My Account Settings of Devolutions Remote Desktop Manager before 2022.1.8 allows authenticated users to access credentials of other users. This issue affects: Dev…
A path traversal issue in entry attachments in Devolutions Remote Desktop Manager before 2022.2 allows attackers to create or overwrite files in an arbitrary location.
A lack of password masking in Devolutions Remote Desktop Manager allows physically proximate attackers to observe sensitive data. A caching issue can cause sensitive fields to sometimes stay revealed …
The biometric lock in Devolutions Password Hub for iOS before 2021.3.4 allows attackers to access the application because of authentication bypass. An attacker must rapidly make failed biometric authe…
An incomplete permission check on entries in Devolutions Remote Desktop Manager before 2021.2.16 allows attackers to bypass permissions via batch custom PowerShell.
Devolutions Server before 2021.1.18, and LTS before 2020.3.20, allows attackers to intercept private keys via a man-in-the-middle attack against the connections/partial endpoint (which accepts clearte…
An SQL Injection issue in Devolutions Server before 2021.1 and Devolutions Server LTS before 2020.3.18 allows an administrative user to execute arbitrary SQL commands via a username in api/security/us…
An overly permissive CORS policy in Devolutions Server before 2021.1 and Devolutions Server LTS before 2020.3.18 allows a remote attacker to leak cross-origin data via a crafted HTML page.
An issue was discovered in Devolutions Server before 2020.3. There is a cross-site scripting (XSS) vulnerability in entries of type Document.
An issue was discovered in Devolutions Server before 2020.3. There is an exposure of sensitive information in diagnostic files.
An issue was discovered in Devolutions Server before 2020.3. There is Broken Authentication with Windows domain users.
An issue was discovered in Devolutions Remote Desktop Manager before 2020.2.12. There is a cross-site scripting (XSS) vulnerability in webviews.
An issue was discovered in Devolutions Server before 2020.3. There is broken access control on Password List entry elements.
Cross-Site Scripting (XSS) in Administrative Reports in Devolutions Remote Desktop Manager before 2021.1 allows remote authenticated users to inject arbitrary web script or HTML via multiple input fie…
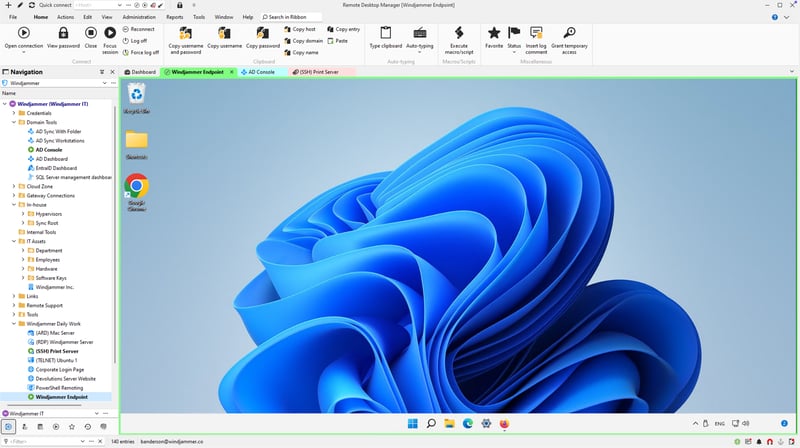
You’ll realize how useful Remote Desktop Manager is when you see how quickly you can login to a customer’s machine that you’ve never worked on before
With Remote Desktop Manager, we’ve enabled our entire team to leverage all of the customer access information that everyone already has
We particularly liked how Remote Desktop Manager offered consolidated, centrally-managed access control and connectivity in a simple to use package
Thanks to RDM, we definitely reduced organizational overhead and improved efficiency and productivity by centrally managing all our connections to our customers
Thanks to RDM, we definitely reduced organizational overhead and improved efficiency and productivity by centrally managing all our connections to our customers. We tested other products, but bought RDM because we thought it was the best product, and we weren’t wrong!
Remote Desktop Manager stands above them all for its ease of use, regular development and integrated tools
Remote Desktop Manager has met and surpassed our expectations…our team is saving a significant amount of time each day
I remain impressed that Devolutions had the foresight to make a great backend SQL solution to support this product
Remote Desktop Manager ha soddisfatto e superato le nostre aspettative… il nostro team risparmia una quantità significativa di tempo ogni giorno