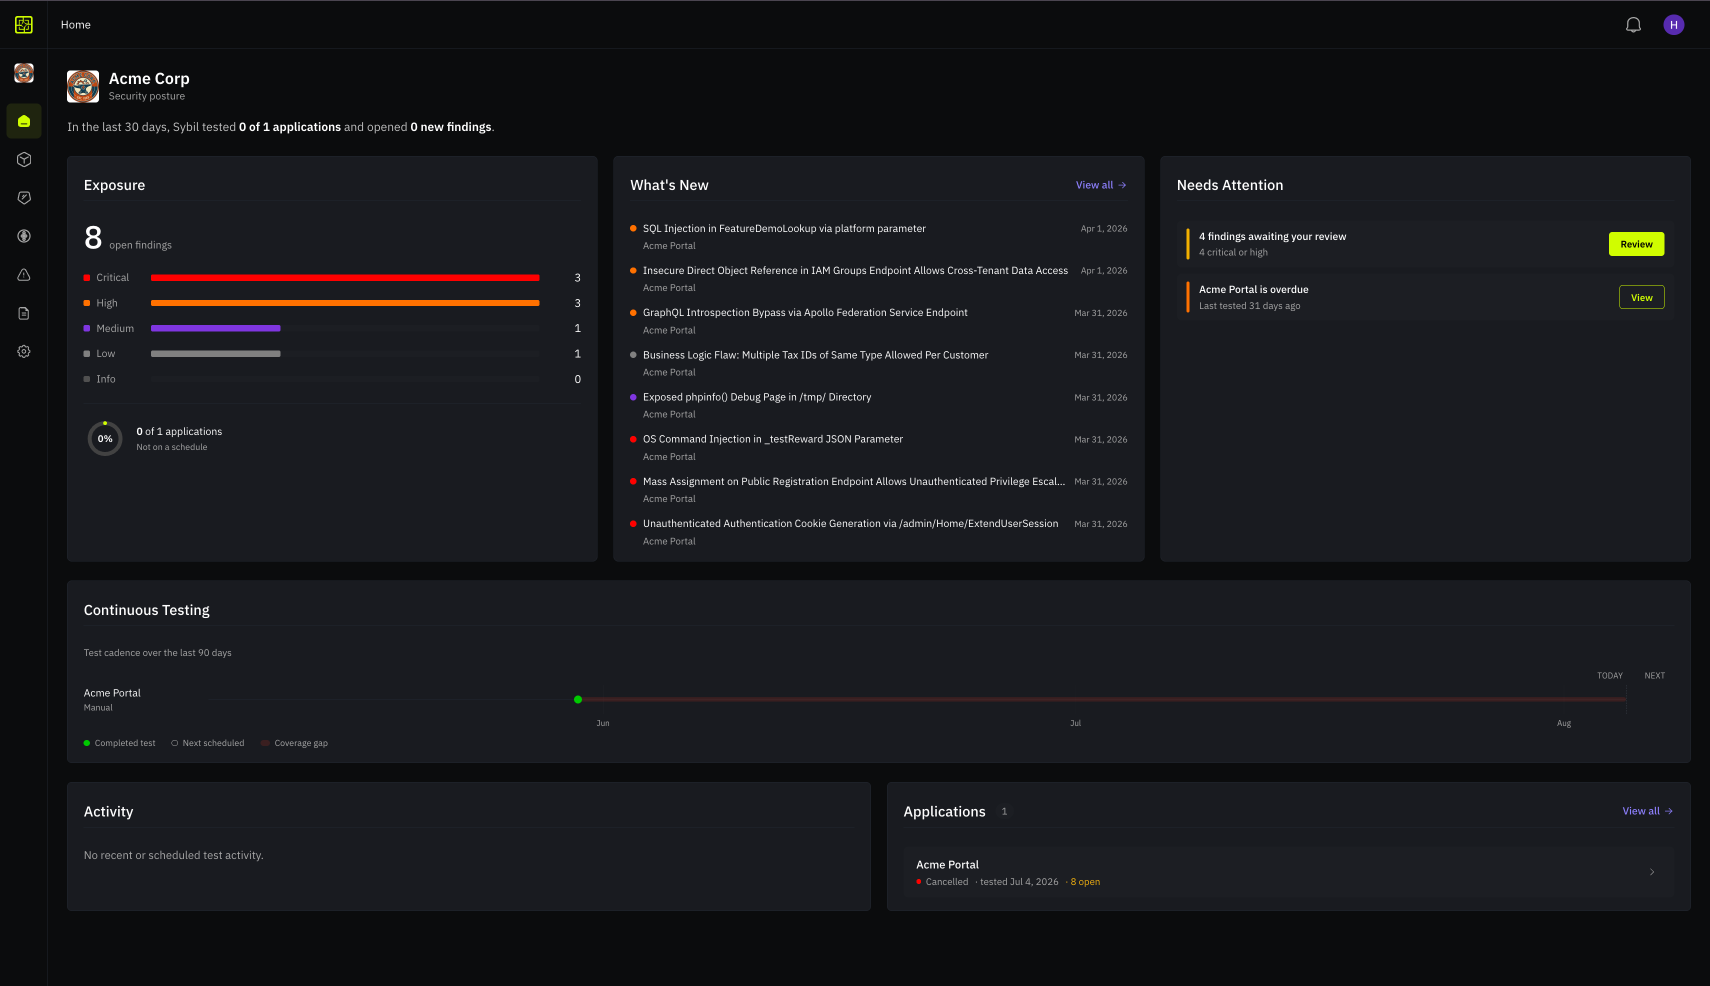
AI-driven continuous attack surface assessment and validation platform.
by RunSybil · runsybil.com · source ↗
RunSybil is an AI-powered offensive security platform that continuously tests applications and infrastructure for exploitable vulnerabilities by reasoning about systems like an elite human researcher. It maps the entire stack across code, APIs, cloud, and infrastructure, chains vulnerabilities to surface real exploitable paths, and re-evaluates continuously with every deployment. The platform supports CTEM by validating whether exposures found by other tools are actually exploitable, delivering pre-validated findings without simulated or periodic testing.
Continuously tests applications and infrastructure for exploitable vulnerabilities Reasons like an attacker to chain vulnerabilities across the stack Covers code, APIs, cloud, and infrastructure Catches vulnerabilities at the commit on every pull request Re-evaluates continuously with every deployment Validates CTEM exposures by proving actual exploitability
No datasheets, whitepapers, case studies, videos, or demos linked yet.