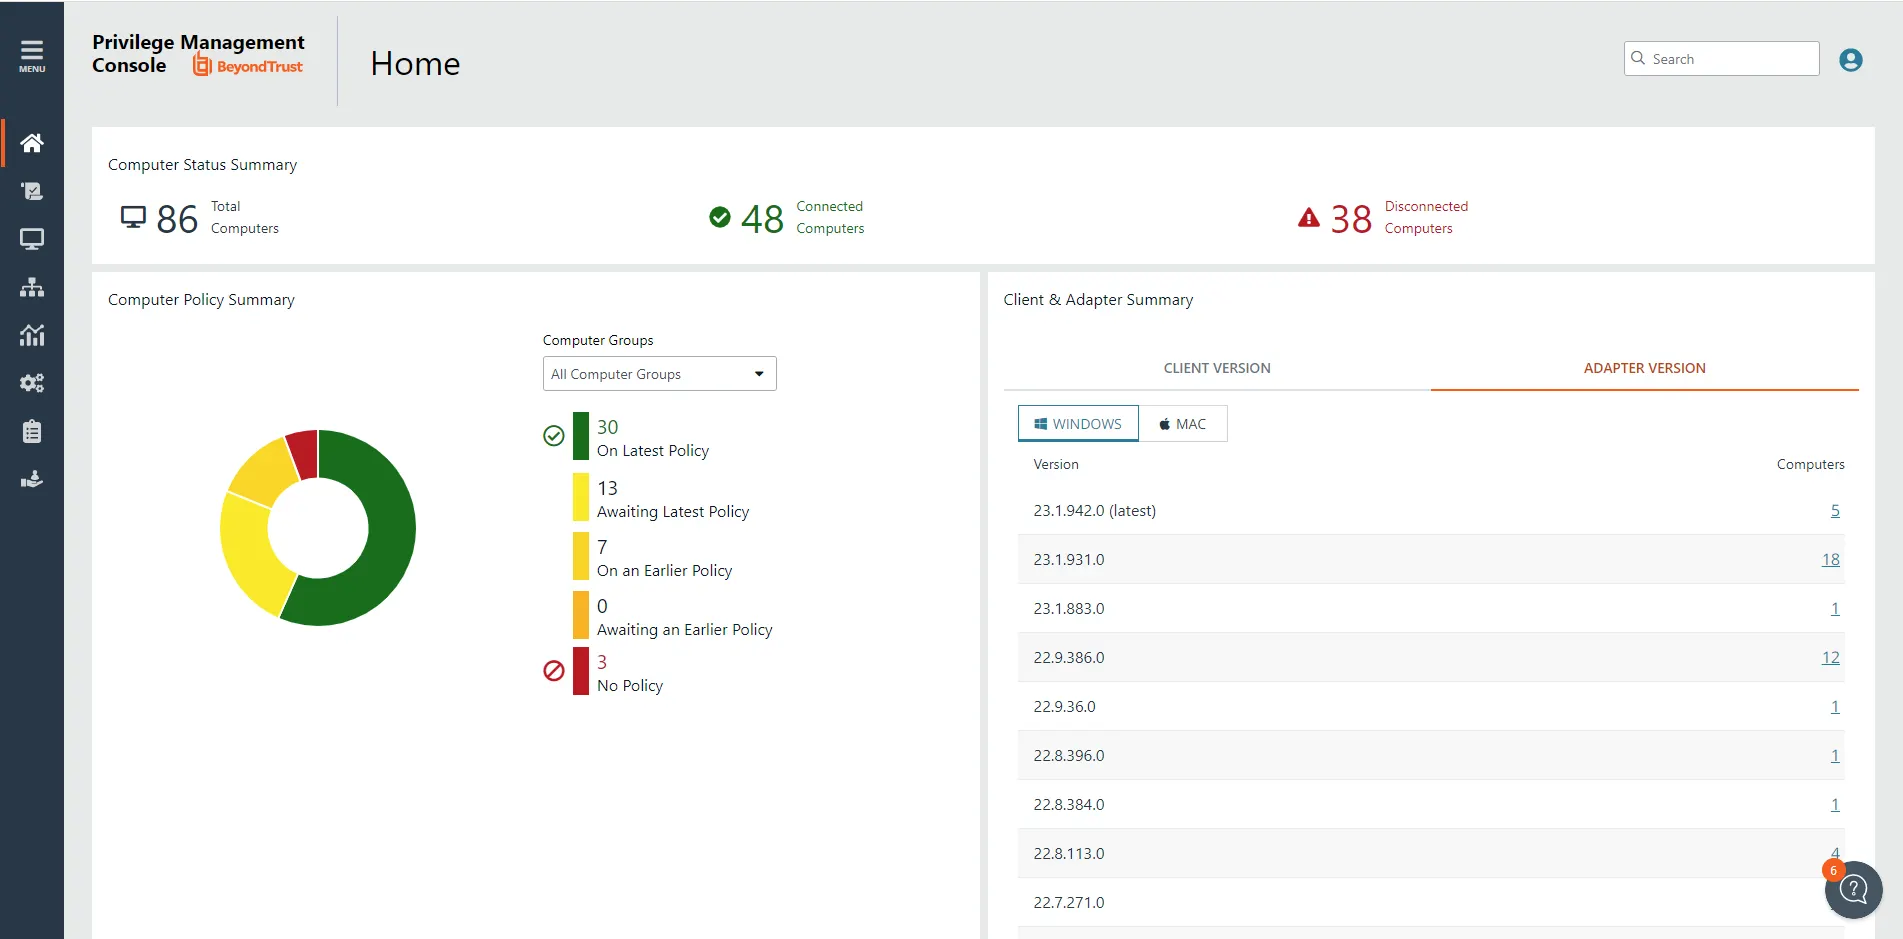
Privileged Access Management solution from BeyondTrust
by BeyondTrust · beyondtrust.com · source ↗
The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the origin of the messages it received. Under the right conditio…
A memory-corruption vulnerability exists in a kernel-mode component of BeyondTrust Endpoint Privilege Management (Windows deployments) prior to version 26.1.2. Insufficient validation of input process…
No datasheets, whitepapers, case studies, videos, or demos linked yet.
A high-severity vulnerability exists in a web application component of BeyondTrust Remote Support and Privileged Remote Access related to the processing of certain input parameters. Insufficient valid…