AI-generated from public sourcesThe starting point for every profile: auto-generated by 0-Doubt from public vendor materials, and not yet confirmed by the vendor or an independent analyst. Nothing here is hidden or overstated — it simply has not been reviewed yet.Where every profile starts, before the vendor or an analyst has reviewed it. A higher label means a more independent source — not a better product.How trust works →Secure coding rating: 52/100How this score is computedA product with no known CVEs starts at a neutral score and climbs the longer it goes without one; a product with known CVEs is penalized by severity instead. This one has 0 known CVEs (vendor-level match — see the CVE list below) and is tracked as ~107 days old in our catalog (a stand-in for real release date, which we don't track). The platform admin controls the formula's weights.
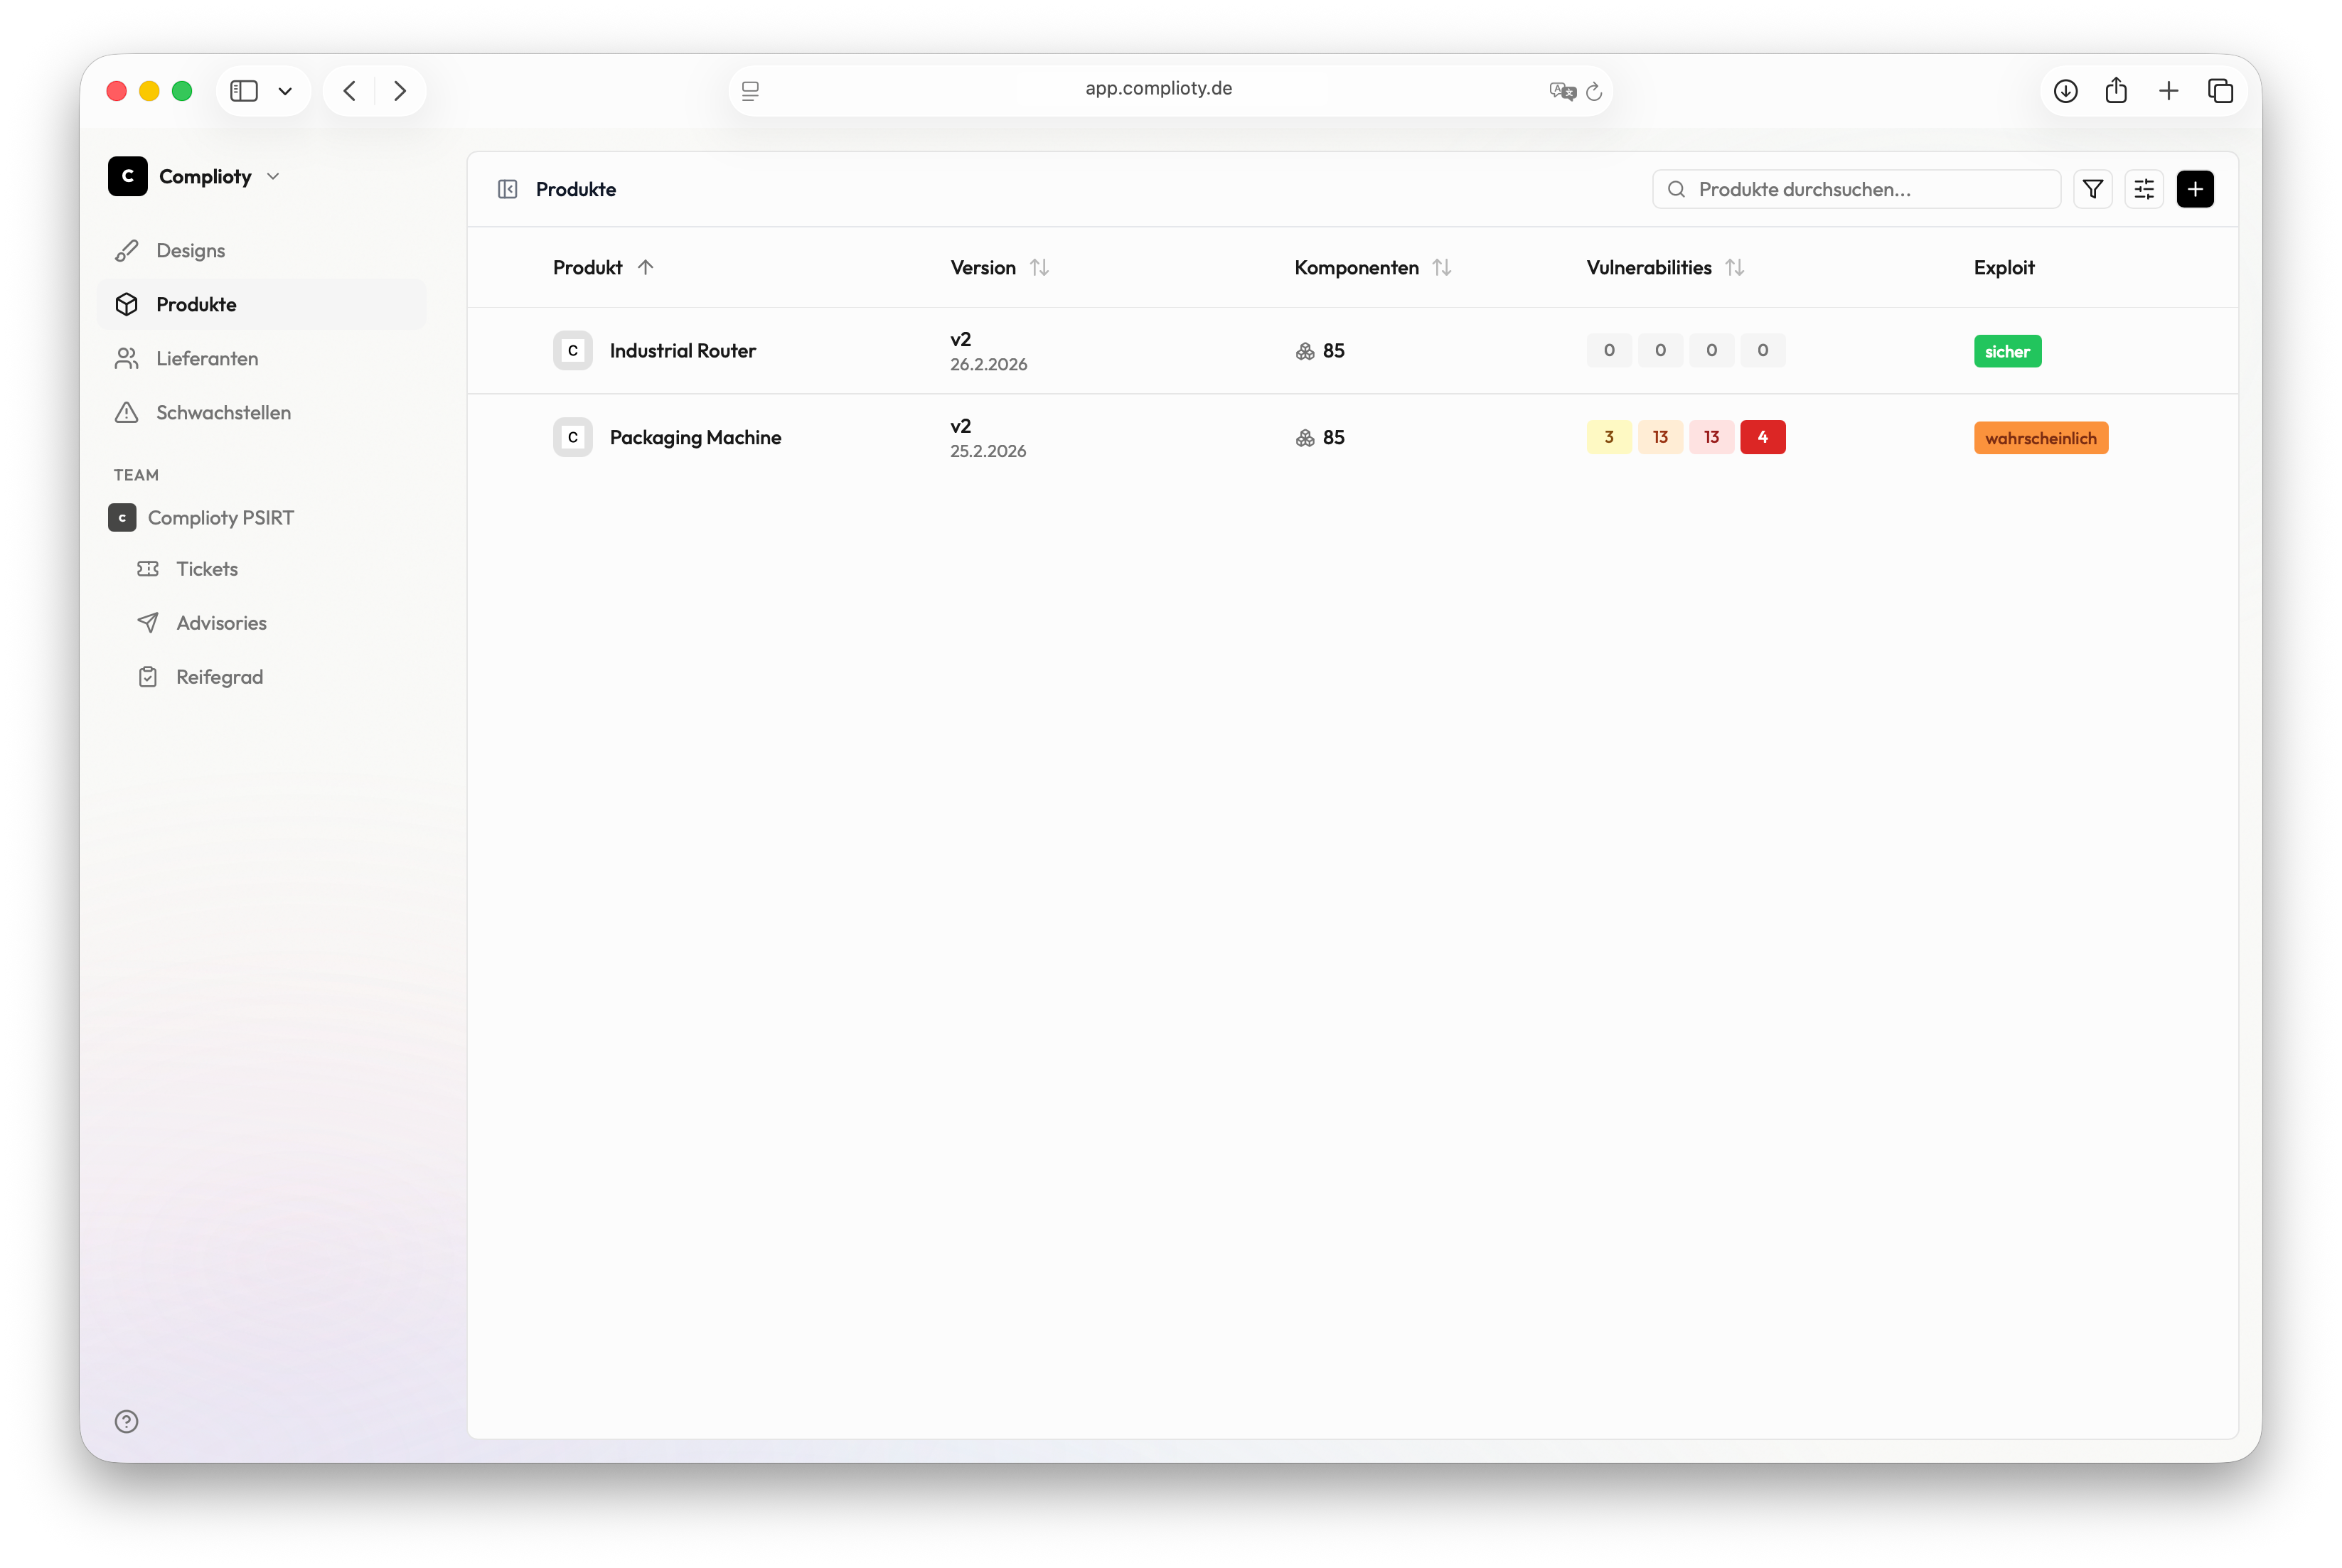
Complioty is a platform that automates Cyber Resilience Act compliance for machine and plant manufacturers, providing automated SBOM creation, CVE monitoring, threat modeling, and supplier management within a single tool.
Strengths
Automated SBOM creation from 20 engineering environments
CVE monitoring with EPSS scoring and exploit detection
Threat modeling linked to actual component architecture
Supplier management with SBOMs and PSIRT status
Customer notification via CSAF-2.0 advisories
Single platform covering SBOM, CVE monitoring, threat modeling, and CVD processes
Materials
0
No datasheets, whitepapers, case studies, videos, or demos linked yet.